A trunk can fail without printing a single error.
The link is up, both switches look configured, and yet no VLAN crosses to the other switch.You are the on-call engineer, and three tickets are waiting in your queue.
For each one you read the symptoms, prove the cause in the CLI, apply the fix, and verify it.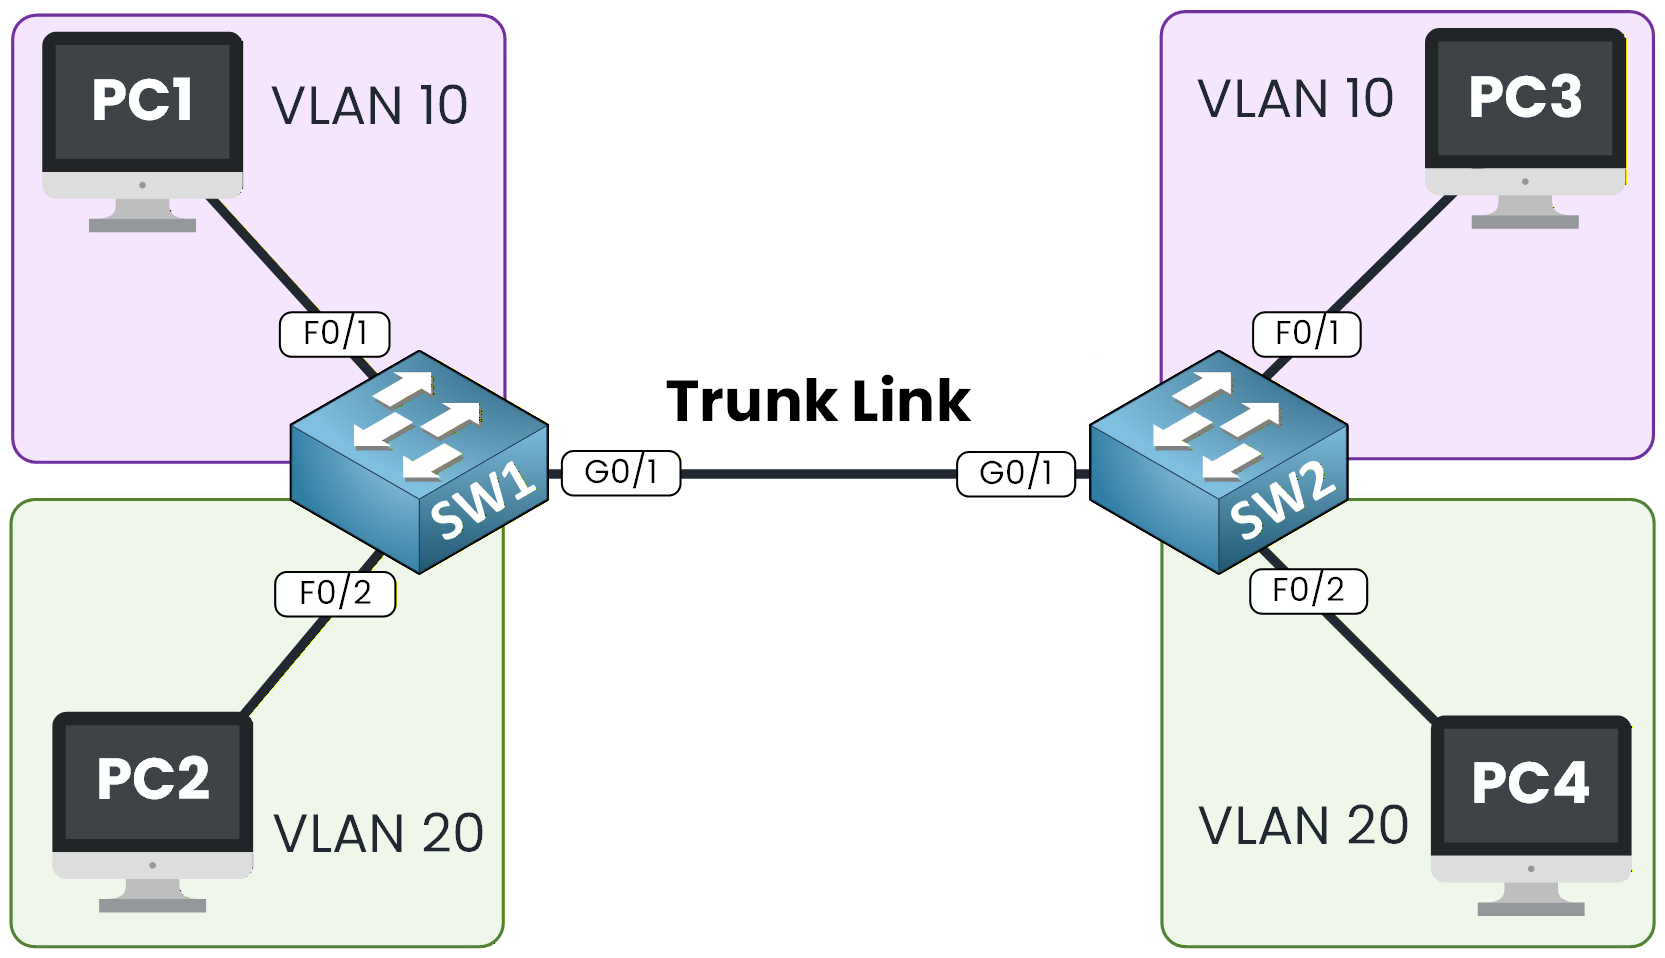
Figure 1 – 802.1Q Lab Topology
Every ticket starts from this topology: SW1 and SW2 joined by a single link on G0/1, VLAN 10 and VLAN 20 on both sides.
Reading the Trunk State
Ticket 1: users in VLAN 10 on SW1 cannot reach VLAN 10 on SW2, and VLAN 20 is dead across the link too.
The cable is fine and both ports are up.Start on SW1: ask it which ports are trunking.
SW1# show interfaces trunk
SW1#
Nothing comes back.
Not a single port is trunking, even though G0/1 is cabled and up.Ask the interface which mode it actually landed in.
SW1# show interfaces g0/1 switchport
Name: Gig0/1
Switchport: Enabled
Administrative Mode: dynamic auto
Operational Mode: static access
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: native
Negotiation of Trunking: On
Access Mode VLAN: 1 (default)
Trunking Native Mode VLAN: 1 (default)
// Output omitted for clarity
Here is the mismatch: the port is set to dynamic auto, yet it came up as static access.
It only trunks if the neighbor initiates, and the neighbor never did.Answer the question below
What is the operational mode of G0/1 while the trunk fails to form?
The Negotiation Deadlock
To see why the trunk never came up, remember how DTP decides.
A dynamic auto port listens for DTP frames but never sends the first one.
When both sides sit in dynamic auto, each one waits for the other to speak.
Nobody initiates, so the link stays access.That is your ticket: dynamic auto on both ends, the one pairing that never trunks.
Two listeners, no speaker.
The full mode matrix lives in the 802.1Q Trunking Review.Answer the question below
Which DTP mode pairing never forms a trunk?
Forcing the Trunk
You could bump one side to dynamic desirable, but on an inter-switch link you want a trunk that never rides on negotiation.
Hardcode both ends as static trunks, so the link never depends on DTP again.SW1# configure terminal Enter configuration commands, one per line. End with CNTL/Z. SW1(config)# interface g0/1 SW1(config-if)# switchport mode trunk SW1(config-if)# end %SYS-5-CONFIG_I: Configured from console by consoleApply the exact same command on SW2, because a static trunk on one side still needs a willing partner on the other.
SW2# configure terminal
Enter configuration commands, one per line. End with CNTL/Z.
SW2(config)# interface g0/1
SW2(config-if)# switchport mode trunk
SW2(config-if)# end
%SYS-5-CONFIG_I: Configured from console by console
Now confirm the trunk is really up on SW1.
SW1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      1

Port        Vlans allowed on trunk
Gi0/1       1-4094

Port        Vlans allowed and active in management domain
Gi0/1       1,10,20
The Status column reads trunking and the mode is on: a static trunk that negotiates nothing.
VLAN 10 and VLAN 20 can finally cross, and both tickets from those users disappear.Both ends now hold the trunk on their own.
You can lock them down further with switchport nonegotiate, a command that stops the port from sending DTP frames entirely.Answer the question below
Which switchport mode forces a trunk without relying on DTP?
Answer the question below
If SW2 were dynamic desirable and SW1 dynamic auto, what Operational Mode would SW1 show?
Ticket 2 is noisy: SW1's console prints the same native VLAN warning every minute.
The trunk is up and tagged VLAN 10 and 20 still work, but untagged traffic is leaking between two VLANs.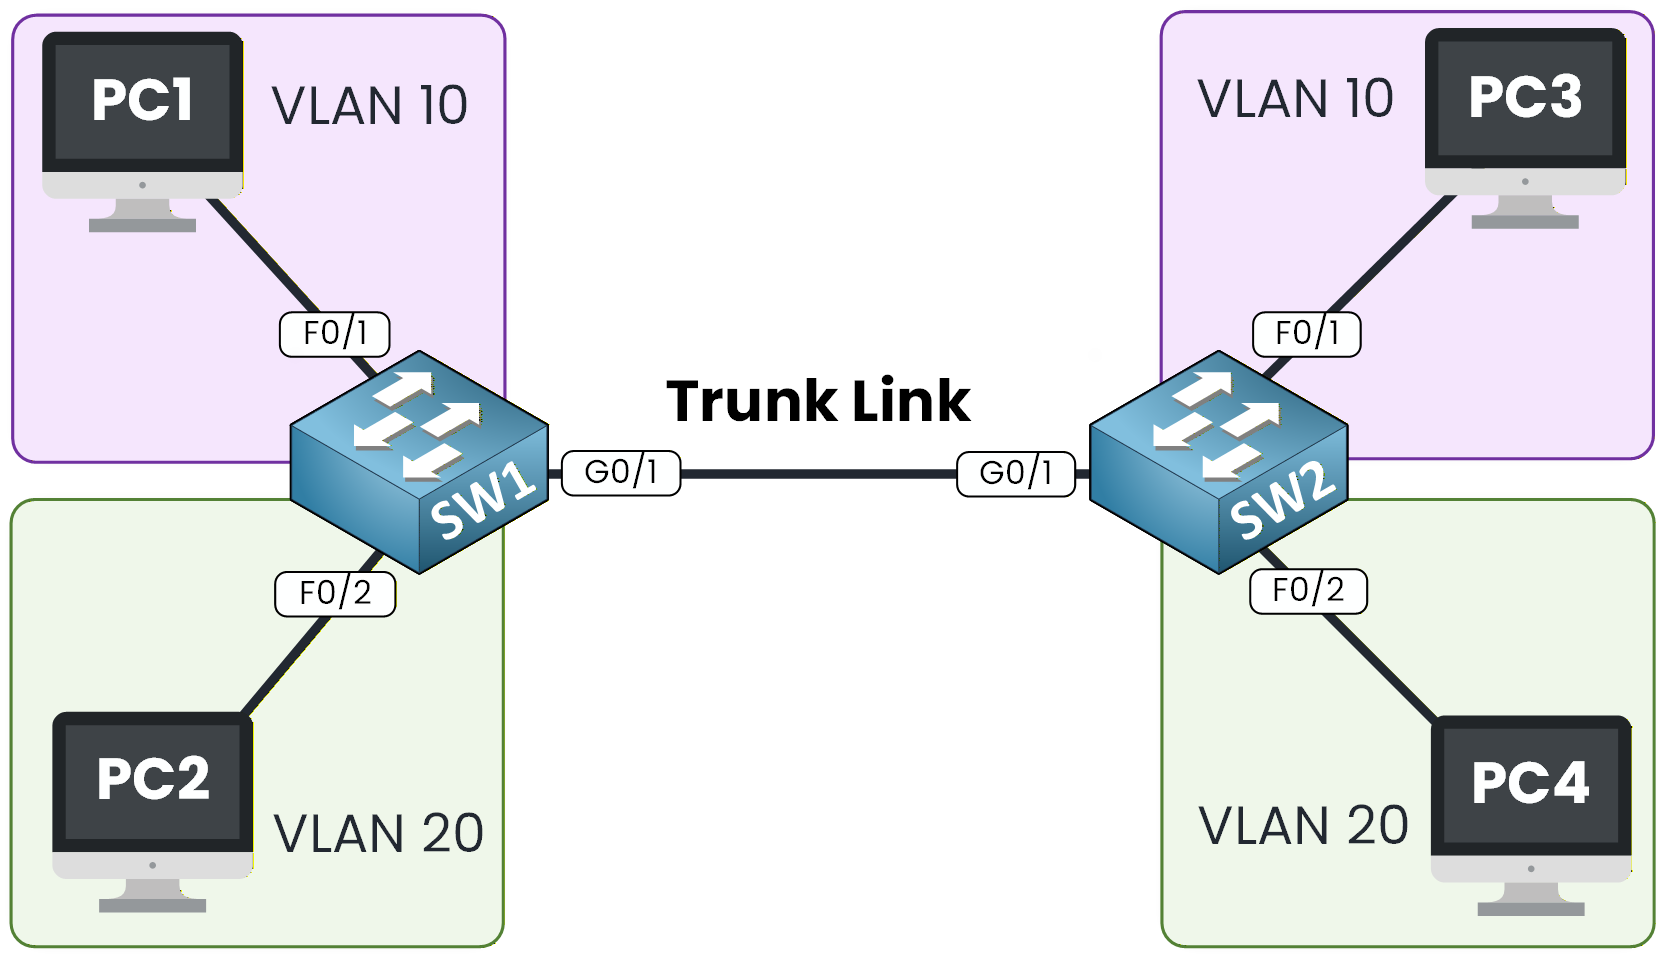
Figure 2 – The Trunk Is Up, but Untagged Traffic Misbehaves
Catching the Log
Start with the warning flooding the console, because it names the mismatch directly.
%CDP-4-NATIVE_VLAN_MISMATCH: Native VLAN mismatch discovered on GigabitEthernet0/1 (1), with SW2 GigabitEthernet0/1 (99).CDP runs by default and compares the native VLAN on each end of the trunk.
Here it flags a difference: SW1 uses native VLAN 1, SW2 uses native VLAN 99.Untagged frames carry no VLAN tag, so each switch drops them into its own native VLAN.
When the two natives differ, untagged traffic crosses from one VLAN into another.
That is exactly what CDP is warning about.Answer the question below
Which protocol raises the native VLAN mismatch warning?
Comparing Both Sides
The log already names the cause, but confirm it from the trunk state on each switch.
SW1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      1

Port        Vlans allowed on trunk
Gi0/1       1-4094
Now the same command on SW2.
SW2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi0/1       1-4094
The Native vlan column confirms the log: 1 on SW1, 99 on SW2.
The trunk still forwards tagged VLAN 10 and 20 fine, which is why only the untagged path misbehaved.Answer the question below
What native VLAN is SW2 using on the trunk?
Aligning the Native VLAN
Both ends must share the same native VLAN.
The safer choice is an unused one like 99 rather than the default 1.
Bring SW1 up to native VLAN 99 so both sides match and untagged frames land in a VLAN no host lives in.SW1# configure terminal Enter configuration commands, one per line. End with CNTL/Z. SW1(config)# interface g0/1 SW1(config-if)# switchport trunk native vlan 99 SW1(config-if)# end %SYS-5-CONFIG_I: Configured from console by consoleVerify both ends now agree.
SW1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi0/1       1-4094
Native VLAN 99 on both sides, and the %CDP-4-NATIVE_VLAN_MISMATCH messages stop the moment CDP sends its next update.
The leak is closed because untagged traffic now sits in an unused VLAN on both switches.Answer the question below
Must the native VLAN be identical on both ends of a trunk?
Ticket 3 is narrower: VLAN 20 users on SW1 cannot reach VLAN 20 on SW2, yet VLAN 10 works perfectly across the very same trunk.
A trunk that carries one VLAN but not another points straight at the allowed list.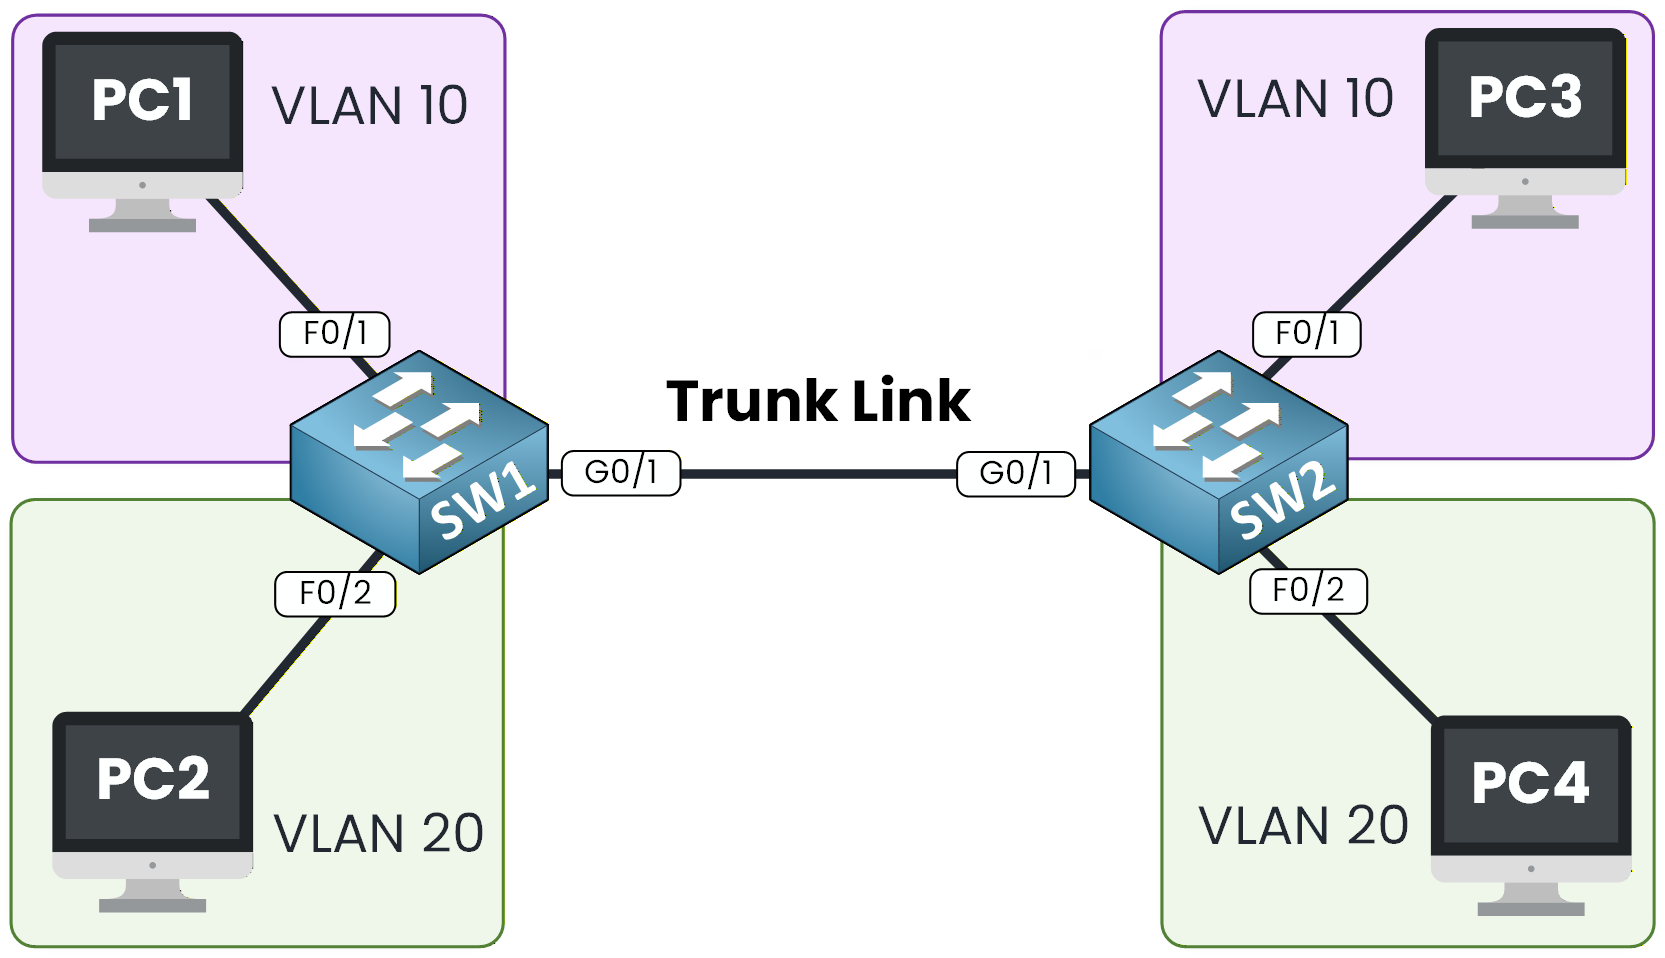
Figure 3 – VLAN 10 crosses the trunk, VLAN 20 does not
Spotting the Gap
When one VLAN crosses and another does not, compare the allowed VLAN list on each end of the trunk.
SW1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi0/1       10,20
Now read the allowed list on SW2.
SW2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi0/1       10
SW1 allows 10 and 20, SW2 allows only 10.
A VLAN filtered off either end of the trunk cannot cross it.
So VLAN 20 is trapped on SW1 while VLAN 10 flows normally.Answer the question below
Which VLAN is missing from the allowed list on SW2?
The add Keyword Trap
You need to add VLAN 20 back on SW2.
One wrong keyword here wipes the trunk.
Typing switchport trunk allowed vlan 20 would replace the whole list and drop VLAN 10 in the process.The add keyword appends without touching the VLANs already there, so it is the safe way to extend a trunk in production.
SW2# configure terminal
Enter configuration commands, one per line. End with CNTL/Z.
SW2(config)# interface g0/1
SW2(config-if)# switchport trunk allowed vlan add 20
SW2(config-if)# end
%SYS-5-CONFIG_I: Configured from console by console
Confirm both VLANs are now allowed on SW2.
SW2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gi0/1       on           802.1q         trunking      99

Port        Vlans allowed on trunk
Gi0/1       10,20
Both ends now allow 10 and 20, and VLAN 20 crosses the trunk exactly like VLAN 10.
The queue is clear.Whatever the trunk ticket, the reflex never changes: check the trunk state on both switches, compare the two sides, fix, then verify.
It is the same discipline you applied in the Troubleshoot EtherChannel lesson, pointed at 802.1Q instead of port-channels.Answer the question below
Which keyword extends a trunk allowed list without removing the current VLANs?
Answer the question below
SW1 allows 10,30 and SW2 allows 20,30, all VLANs created: which VLAN crosses the trunk?