Have you ever wondered what BPDU Guard is and how it protects your network?
Let’s make it simple and start with an example.In the diagram below, we see a typical STP topology with three switches: SW1, SW2, and SW3.
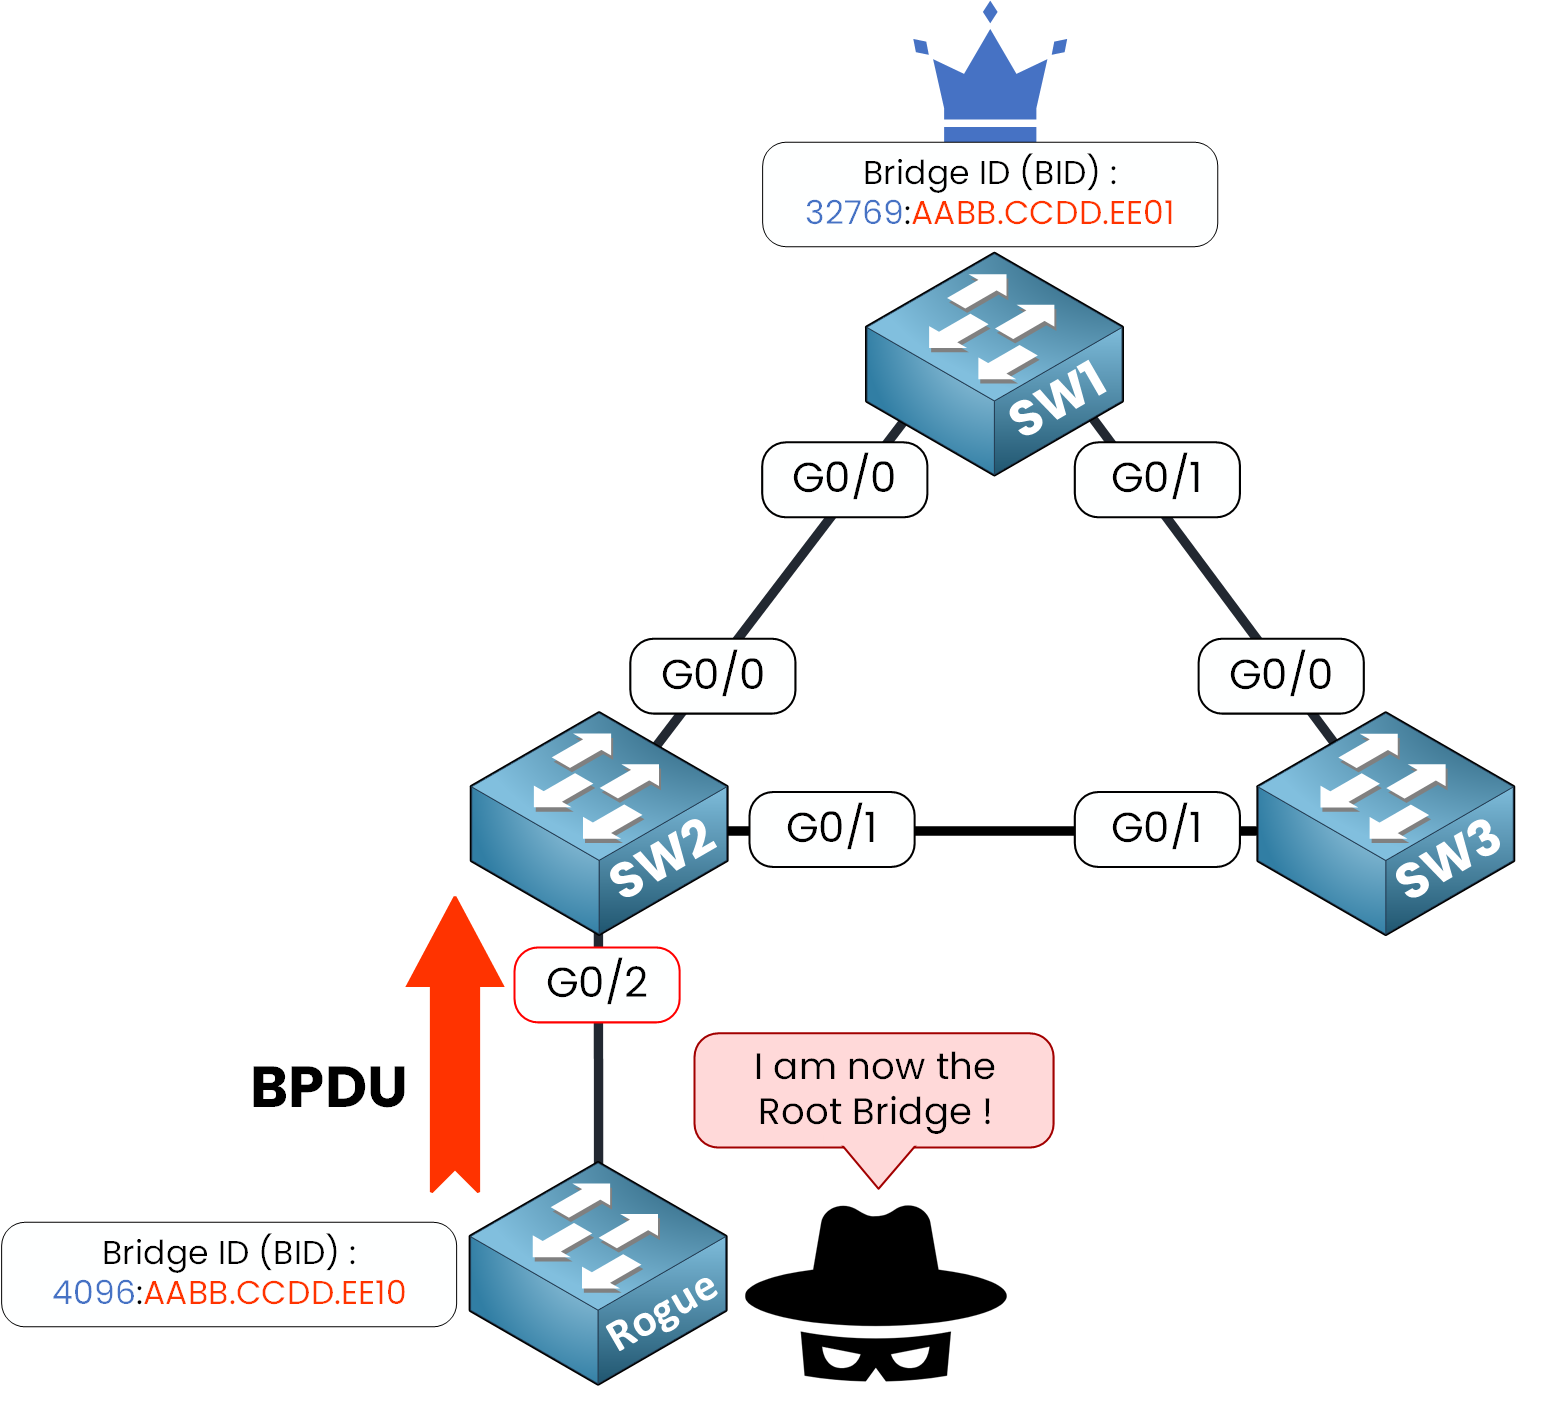
Figure 1 – Rogue switch sends BPDUs to claim Root Bridge role
SW1 is the Root Bridge, with Bridge ID
32769:AABB.CCDD.EE01SW2 has a port (G0/2) configured with PortFast, normally meant for end devices.
But here's the problem:
A rogue switch gets connected to that access port!
Instead of staying quiet, it sends BPDUs with a lower Bridge Priority:4096:AABB.CCDD.EE10, which is better than the current Root Bridge.Since BPDU Guard is not enabled, SW2 accepts the BPDU and forwards the BPDU into the STP topology.
Without BPDU Guard
The Rogue Switch wins the Root Bridge Election because it advertises a better priority
4096against SW1's priority32769. It is now selected as the new Root Bridge.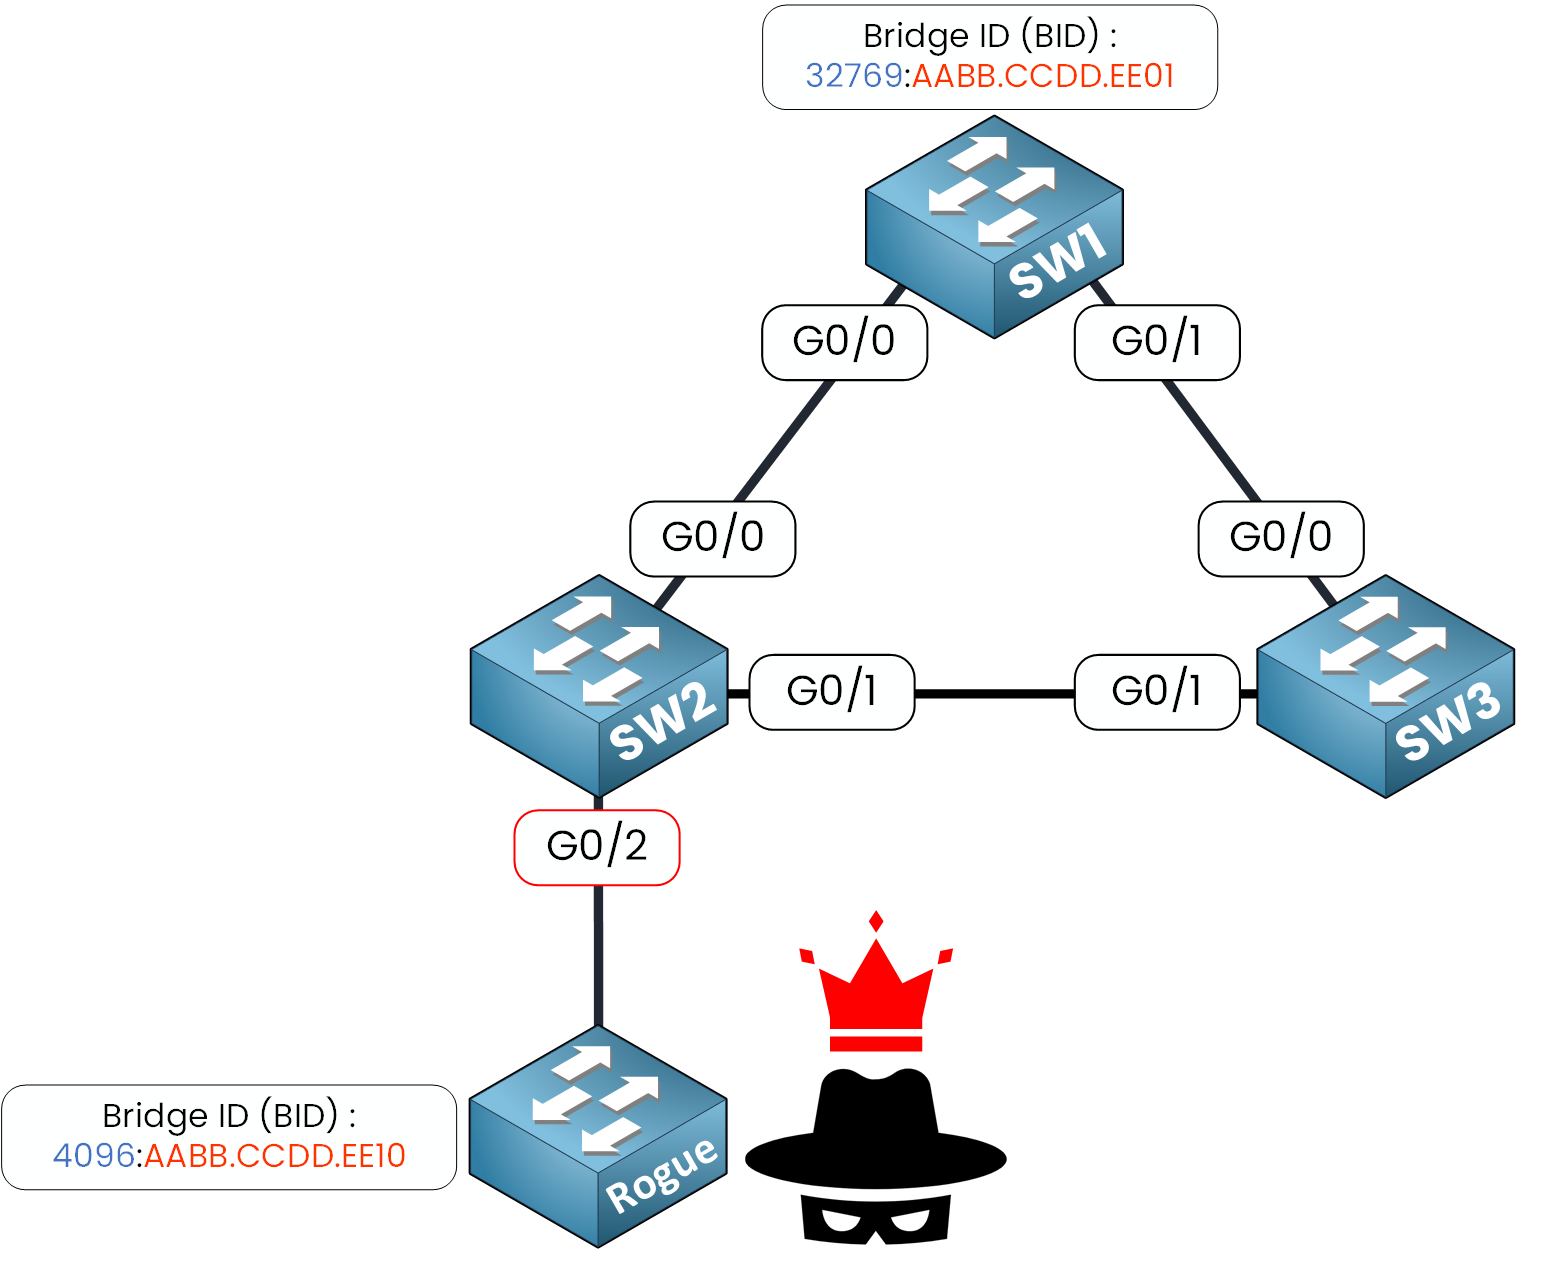
Figure 2 – Rogue switch becomes Root Bridge by sending superior BPDUs
Your entire Spanning Tree topology is now compromised and all of this started from a single access port not properly secured... This is exactly what the BPDU Guard feature is designed to prevent.
Solution: Enabling BPDU Guard
To prevent this situation, BPDU Guard must be applied to the PortFast-enabled port.
BPDU Guard discards any incoming BPDU and places the port into an err-disable state (down/down).This ensures that access ports, typically connected to end-user devices like PCs or printers, can’t participate in STP.
With BPDU Guard
Let's review our example with BPDU Guard enabled on the interface connected to the rogue switch.
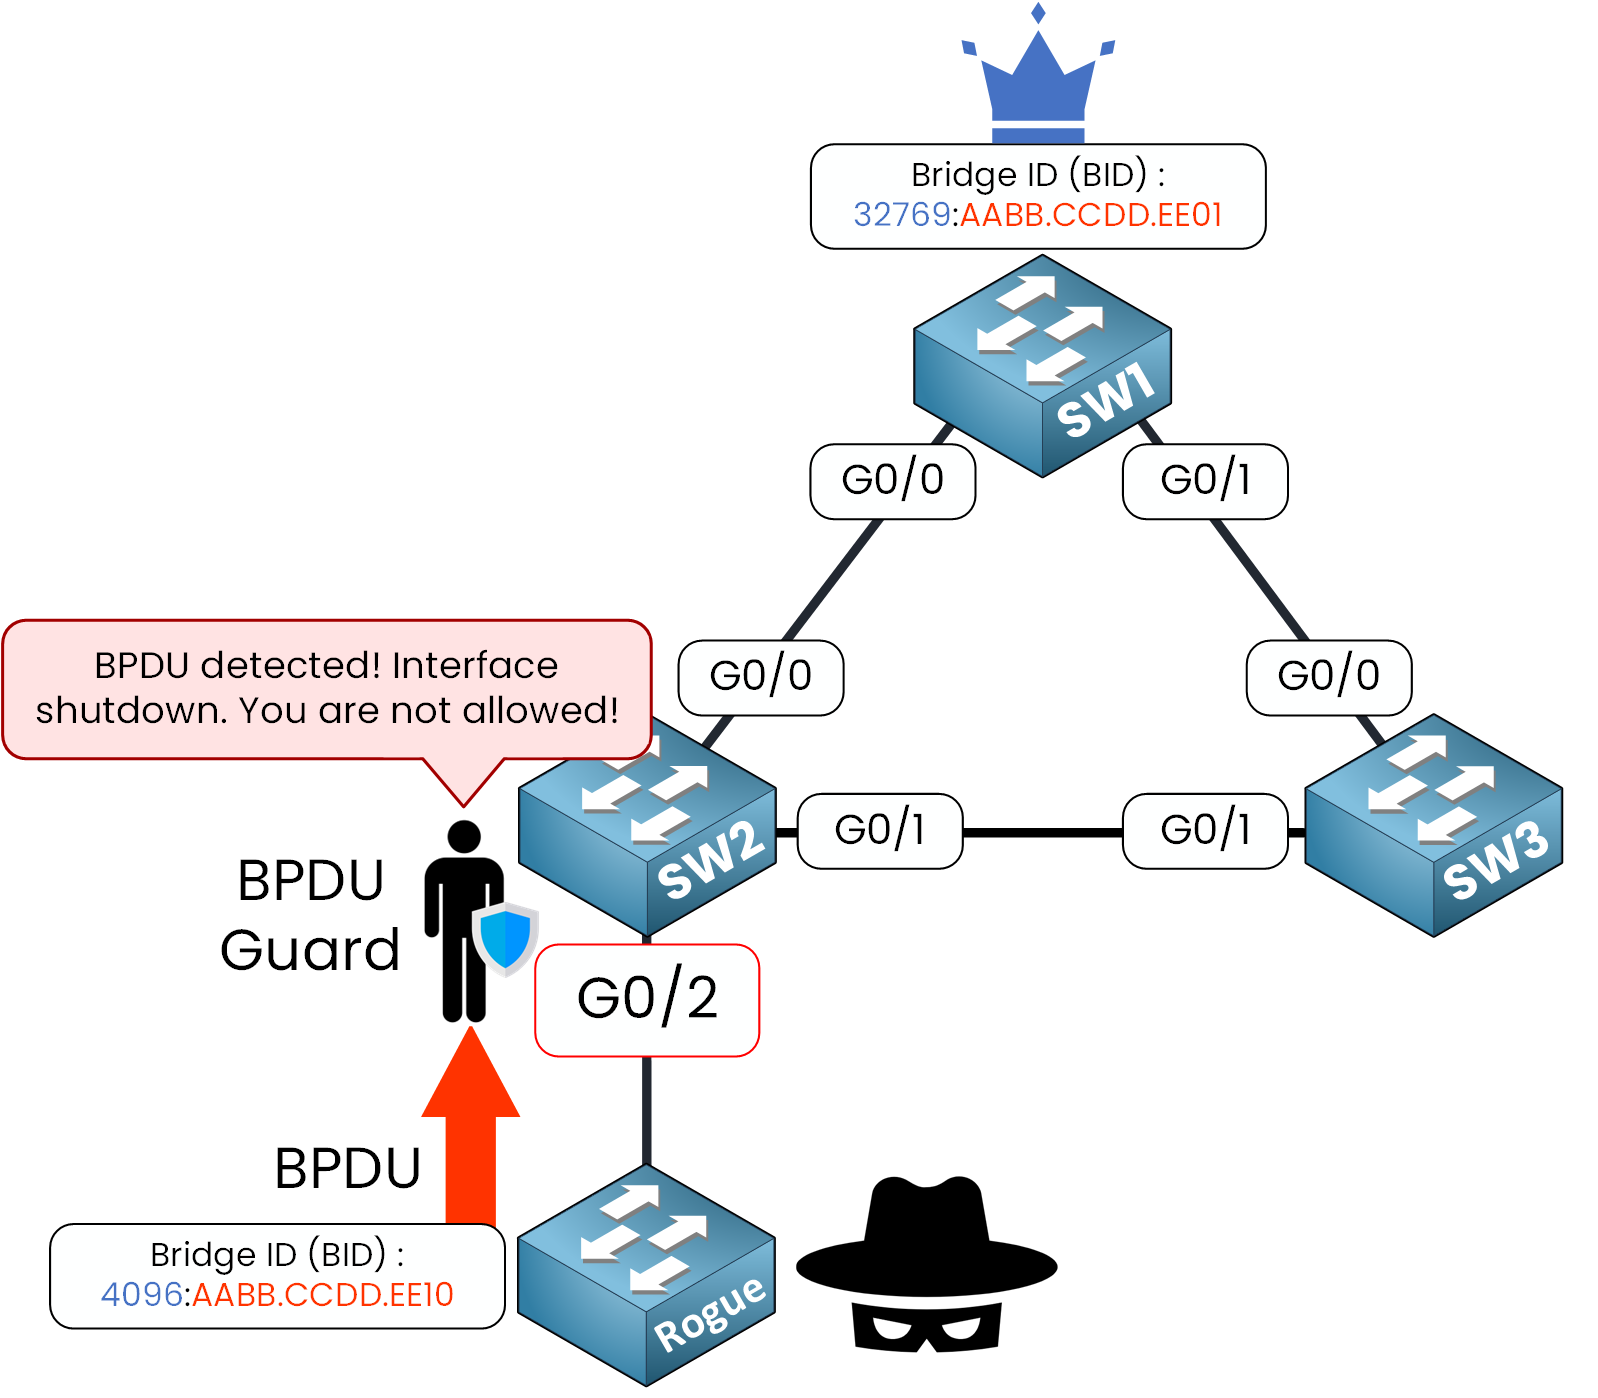
Figure 3 – BPDU Guard blocks the rogue switch by shutting down the interface
The BPDU Guard feature detects the incoming BPDU on the interface and immediately disables the port to protect the network.
*Dec  8 12:58:28.065: %SPANTREE-2-BLOCK_BPDUGUARD: Received BPDU on port Gi0/2 with BPDU Guard enabled. Disabling port.

*Dec  8 12:58:28.066: %PM-4-ERR_DISABLE: bpduguard error detected on Gi0/2, putting Gi0/2 in err-disable state

*Dec  8 12:58:29.073: %LINEPROTO-5-UPDOWN: Line protocol on Interface GigabitEthernet0/2, changed state to down

*Dec  8 12:58:30.109: %LINK-3-UPDOWN: Interface GigabitEthernet0/2, changed state to down
As you can see above, a BPDU was received on interface G0/2 with BPDU Guard enabled, and this event triggers the shutdown of the interface.
Answer the question below
What does the rogue switch try to become by sending superior BPDUs?
Before diving into the configuration, let's clarify an important point: BPDU Guard and PortFast are separate features.
While they are often used together, they can be configured independently based on your network requirements.If you want end-user devices (like PCs or printers) to access the network instantly and be protected from rogue switches, you should activate both PortFast and BPDU Guard on the same port.
In this example, we will configure:
PortFast to skip the usual STP State delay.
BPDU Guard to shut down the port if an unexpected BPDU is received.
Let's apply the PortFast Feature first on interface G0/2:
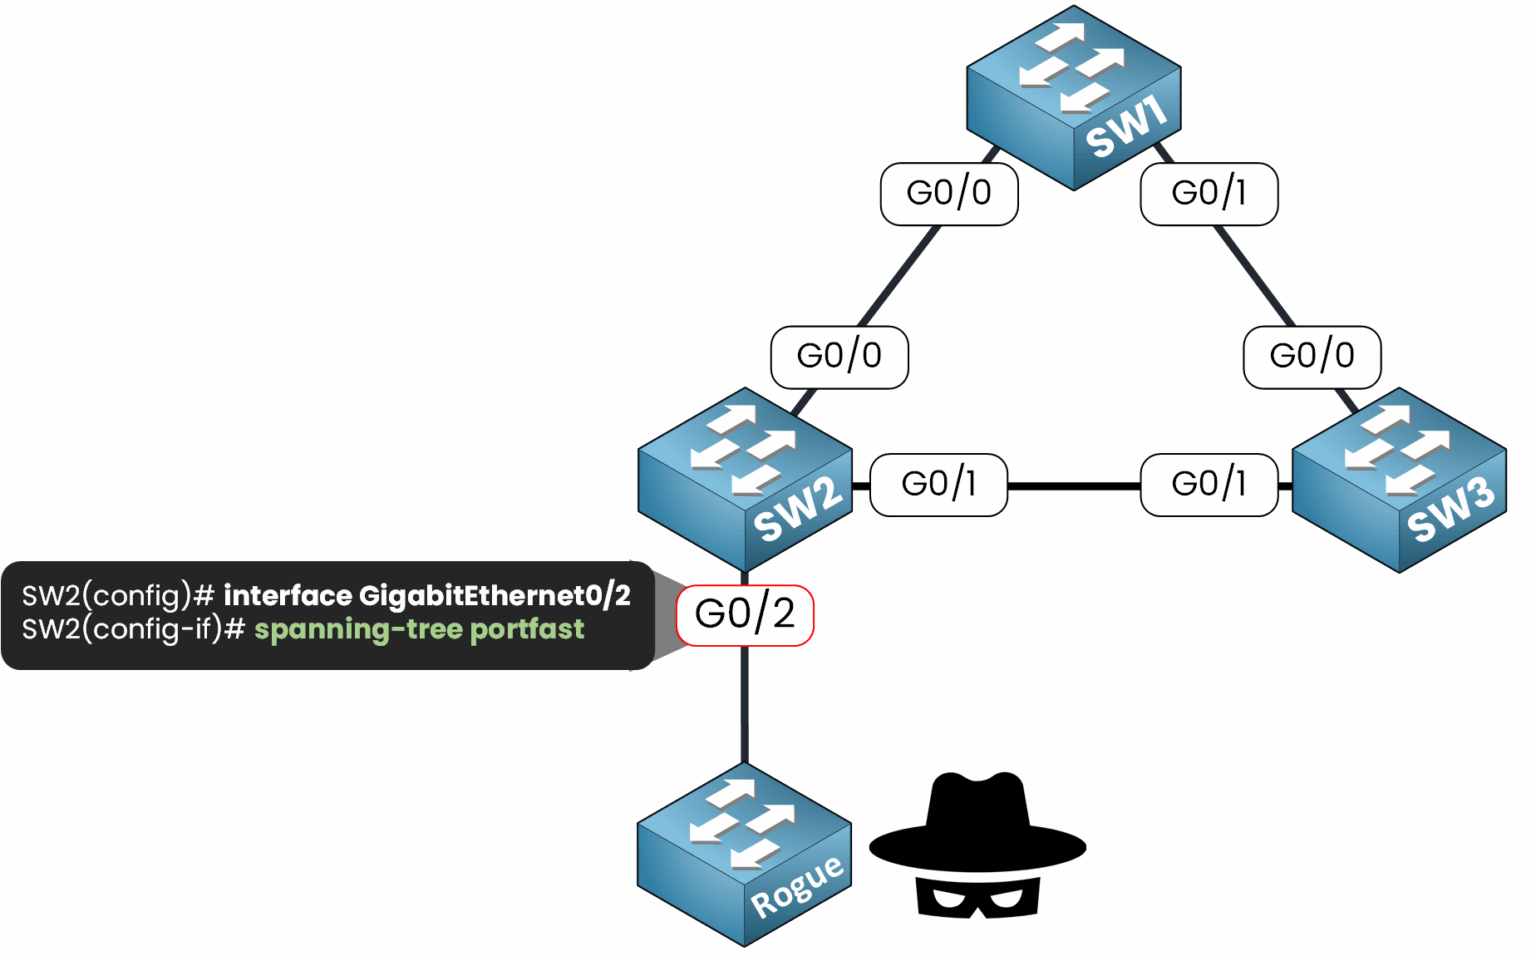
Figure 4 – Configuring PortFast on SW2 interface G0/2 before enabling BPDU Guard
Now we can configure BPDU Guard.
BPDU Guard can be configured in two ways:
On Individual Ports: Applied manually to each specific port.
Globally: Automatically applied to all interfaces already configured with PortFast.
Enabling BPDU Guard on Individual Ports
1. Enter interface configuration mode:
SW2# conf t
Enter configuration commands, one per line.  End with CNTL/Z.
SW2(config)# int g0/2
2. Enable BPDU Guard on the interface:
SW2(config-if)# spanning-tree bpduguard enable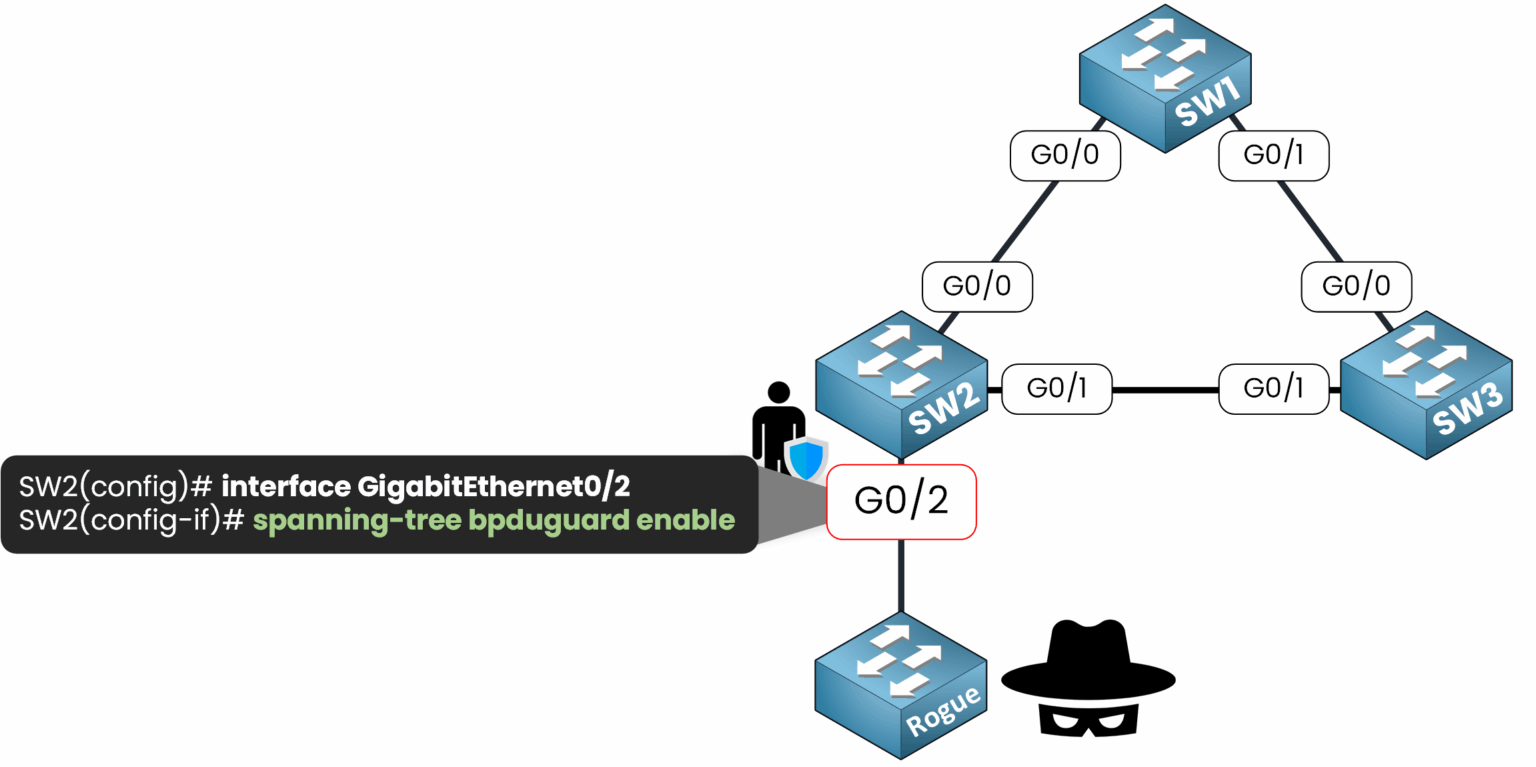
Figure 5 – Enabling BPDU Guard on interface G0/2
Verifying BPDU Guard Status
To confirm BPDU Guard is enabled and active, we can use the
show spanning-tree interface g0/2 detailcommand:SW2# end %SYS-5-CONFIG_I: Configured from console by console SW2# show spanning-tree interface g0/2 detail Port 3 (GigabitEthernet0/2) of VLAN0001 is designated forwarding Port path cost 4, Port priority 128, Port Identifier 128.3. Designated root has priority 32769, address 50e2.aa04.6b00 Designated bridge has priority 32769, address 50e2.aa04.6b00 Designated port id is 128.3, designated path cost 0 Timers: message age 0, forward delay 0, hold 0 Number of transitions to forwarding state: 1 The port is in the portfast edge mode Link type is point-to-point by default Bpdu guard is enabled BPDU: sent 3, received 0As you can see in the output, the BPDU Guard feature is enabled!
Behavior When a BPDU is Received
Let's revisit our example: the Rogue Switch sends a BPDU and BPDU Guard is enabled:
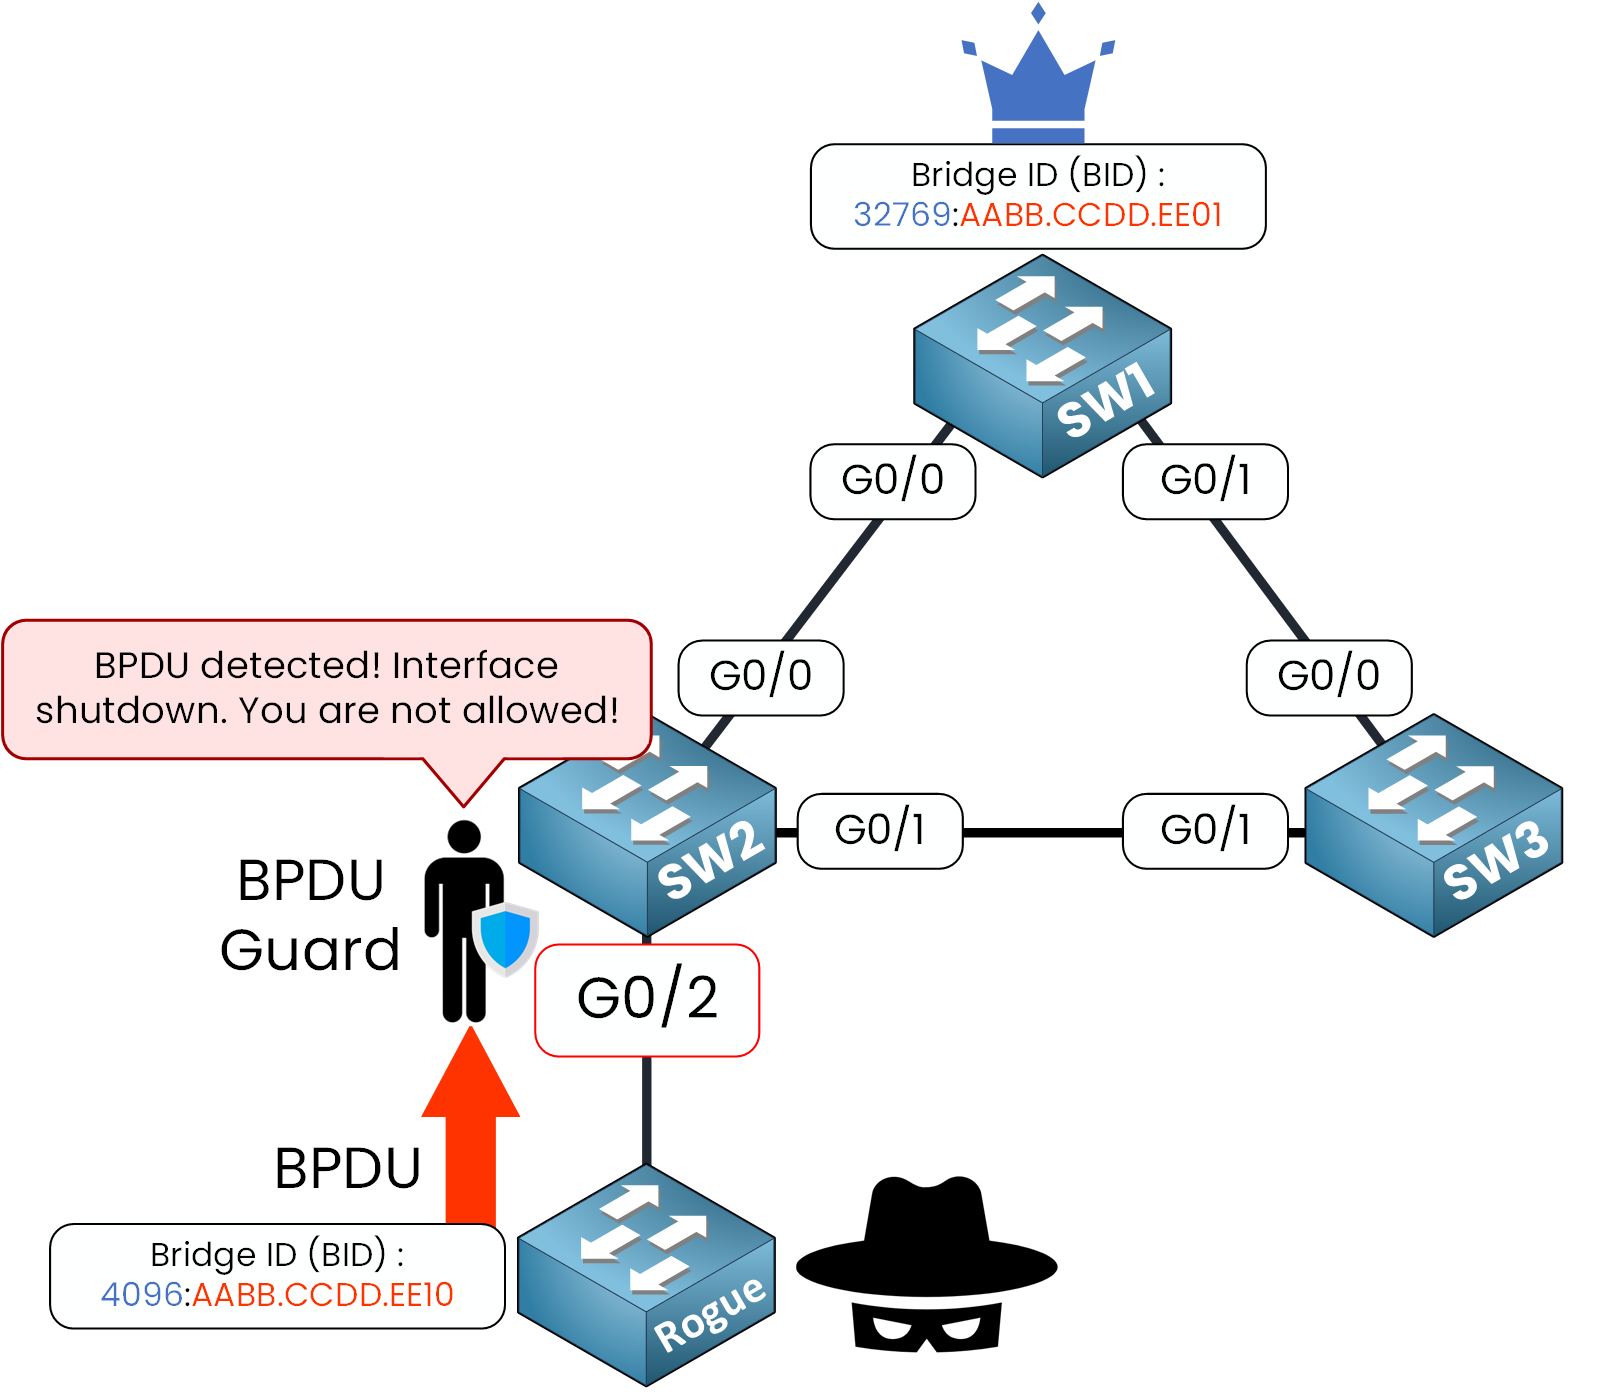
Figure 6 – BPDU Guard shuts down the port and places it in err-disabled state
The interface is immediately
shut down and placed into an err-disabled state.You can verify this by looking at the interface status:
SW2# show int g0/2
GigabitEthernet0/2 is down, line protocol is down (err-disabled)
!output omitted
The line protocol is down and the err-disabled state appears as expected.
Disabling BPDU Guard on Individual Ports
In some situations, you may need to disable BPDU Guard on a specific interface. This can be done directly in interface configuration mode:
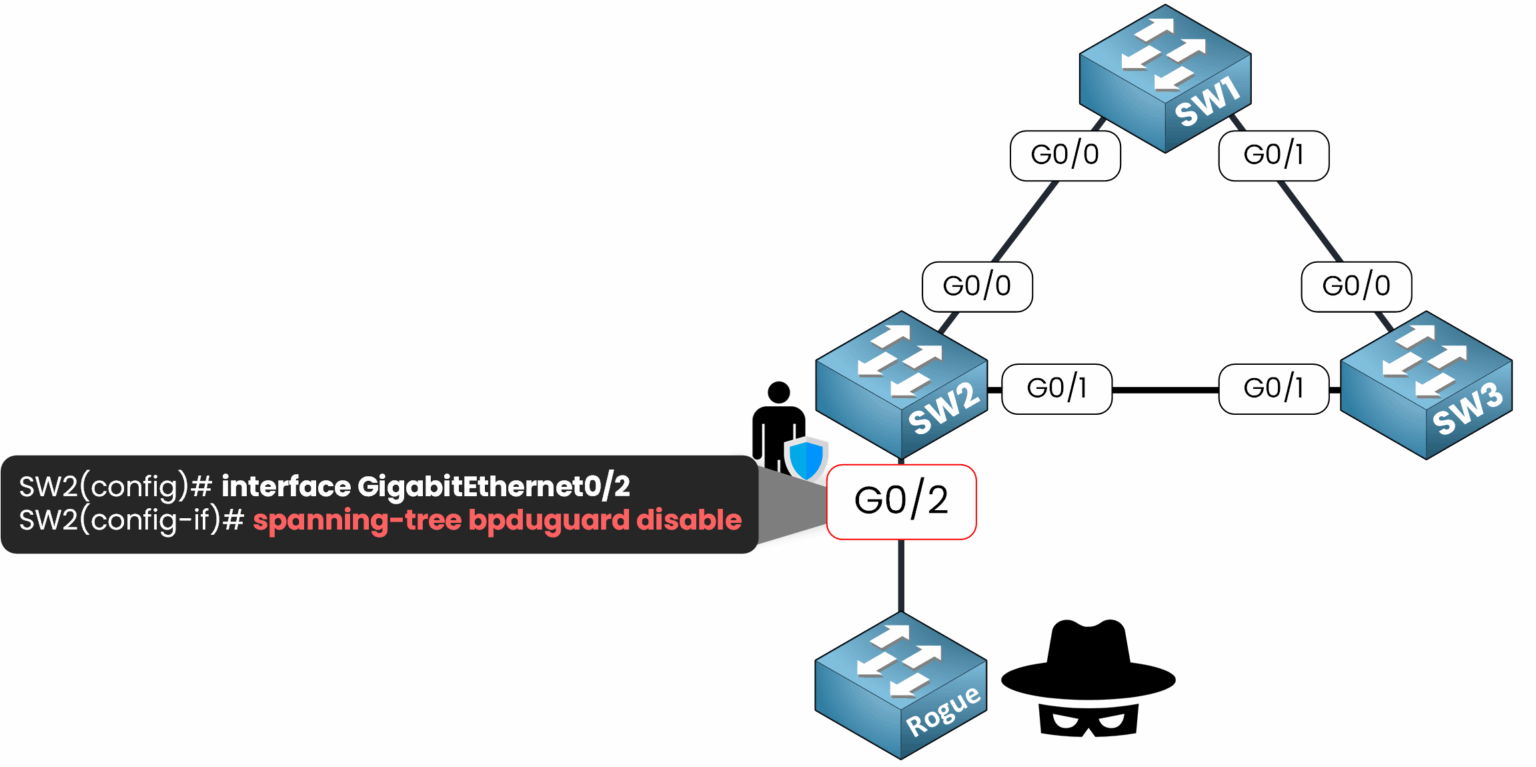
Figure 7 – Disabling BPDU Guard on SW2 interface G0/2
SW2# conf t
Enter configuration commands, one per line.  End with CNTL/Z.
SW2(config)# int g0/2
SW2(config-if)# spanning-tree bpduguard disable
SW2(config-if)# exit
This command removes BPDU Guard protection from the selected port only.
Enabling BPDU Guard Globally
BPDU Guard can also be enabled globally, allowing it to be automatically applied to all interfaces configured with PortFast.
SW2(config)# spanning-tree portfast bpduguard defaultBefore applying this command, make sure to review which interfaces on your switch are configured with PortFast. BPDU Guard will be automatically applied to all of them.
Answer the question below
Which feature is commonly paired with BPDU Guard?
We have seen that when BPDU Guard detects a BPDU, it immediately shuts the port down to protect the network.
The interface enters theerr-disabled state with a status of down/down.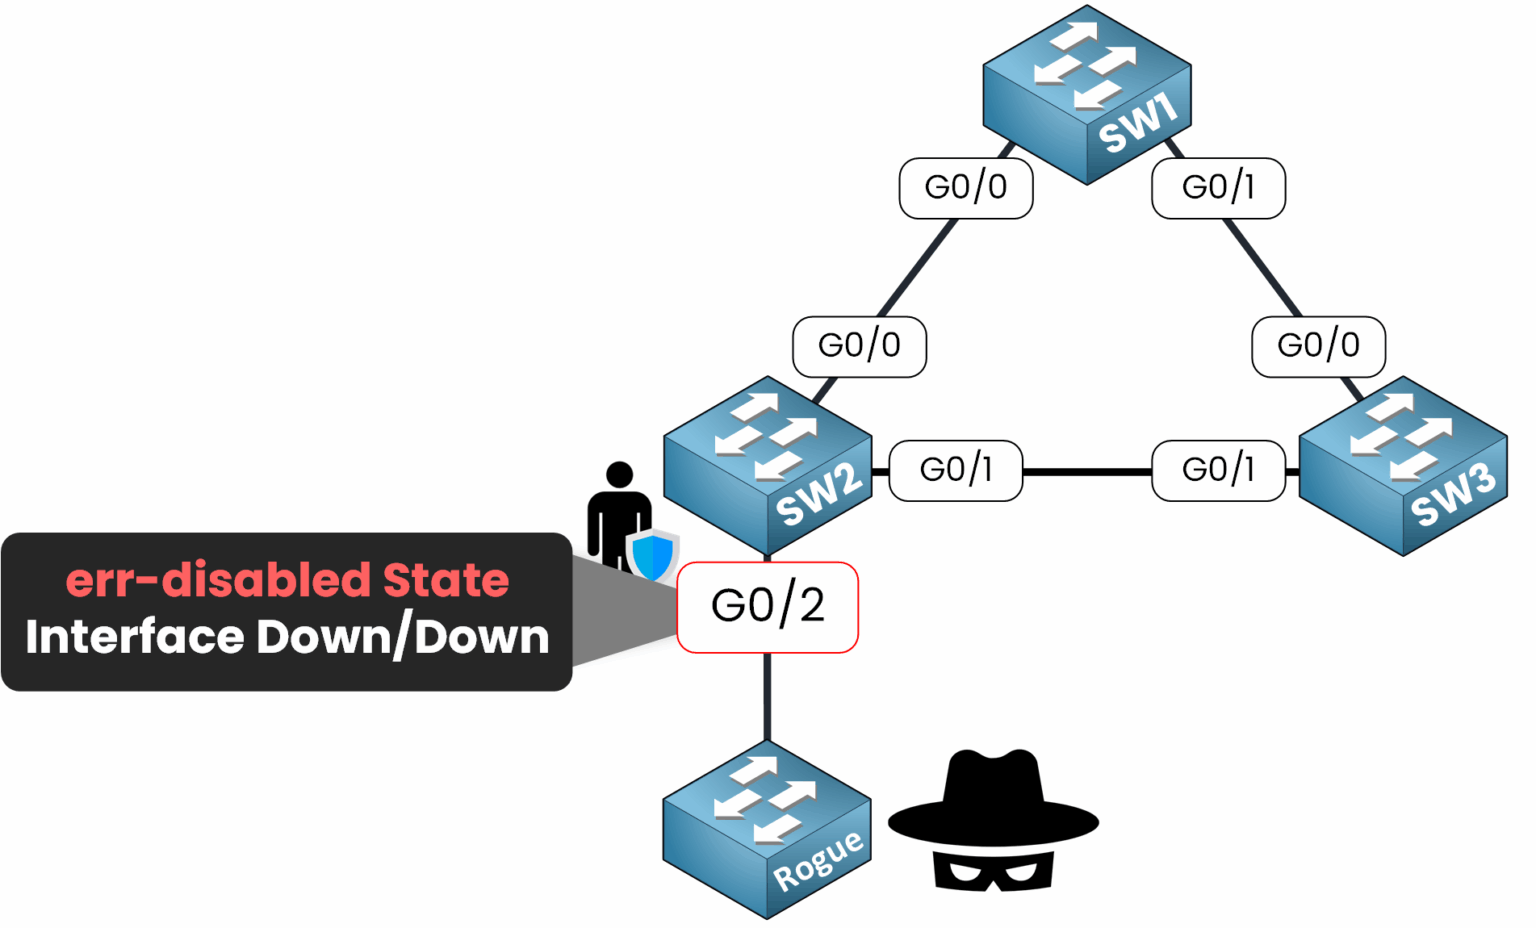
Figure 8 – Interface enters err-disabled state after receiving BPDU from rogue switch
Now that the interface is down, as a Network Engineer you need to remove the Rogue Device before attempting to recover the interface. Then you can recover the port by using one of the two recovery methods for ErrDisable State.
Answer the question below
When BPDU Guard detects a BPDU on a protected port, what state does the interface enter?
The first method we'll look at is Manual Recovery, and it's very simple:
Manual Recovery
You can reset the port manually by using the
shutdownandno shutdowncommands:SW2# conf t Enter configuration commands, one per line. End with CNTL/Z. SW2(config)# interface g0/2 SW2(config-if)# shutdown %LINK-5-CHANGED: Interface GigabitEthernet0/2, changed state to administratively down %LINEPROTO-5-UPDOWN: Line protocol on Interface GigabitEthernet0/2, changed state to down SW2(config-if)# no shutdown %LINK-5-CHANGED: Interface GigabitEthernet0/2, changed state to up %LINEPROTO-5-UPDOWN: Line protocol on Interface GigabitEthernet0/2, changed state to upThe interface will return to the UP/UP state, and if no rogue device sends BPDUs again, it will remain operational.
SW2(config-if)# end
%SYS-5-CONFIG_I: Configured from console by console

SW2# show int g0/2
GigabitEthernet0/2 is up, line protocol is up (connected)
!output omitted
Automatic Recovery (ErrDisable Recovery)
The second method is Automatic Recovery, also known as ErrDisable Recovery. Cisco switches can recover ports automatically 300 seconds after the event.
By default, this mechanism is disabled. You can check its current status with the
show errdisable recoverycommand:SW2# show errdisable recovery ErrDisable Reason Timer Status ----------------- -------------- arp-inspection Disabled bpduguard Disabled !output omitted Timer interval: 300 seconds Interfaces that will be enabled at the next timeout:Here you can see ErrDisable Reason for bpduguard is disabled.
Enabling Automatic Recovery
To enable ErrDisable Recovery for the bpduguard cause, we use:
SW2# conf t
Enter configuration commands, one per line.  End with CNTL/Z.
SW2(config)# errdisable recovery cause bpduguard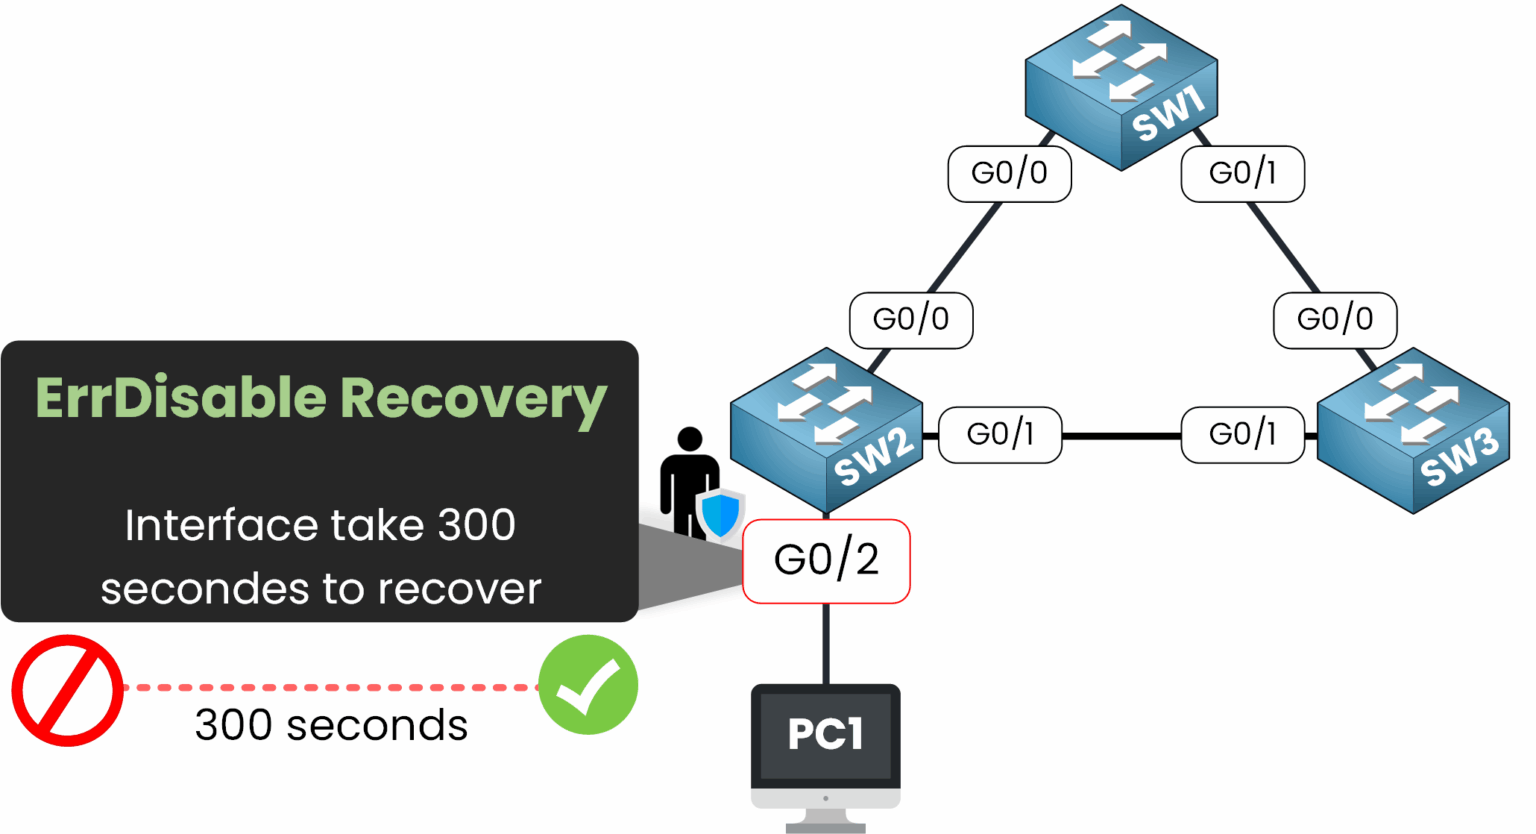
Figure 9 – ErrDisable Recovery automatically re-enables the port after 300 seconds
The BPDU Guard cause for recovery is enabled:
SW2(config-if)# end
%SYS-5-CONFIG_I: Configured from console by console
SW2# show errdisable recovery
ErrDisable Reason            Timer Status
-----------------            --------------
arp-inspection               Disabled
bpduguard                    Enabled
!output omitted

Timer interval: 300 seconds

Interfaces that will be enabled at the next timeout:

Interface       Errdisable reason       Time left(sec)
---------       -----------------       --------------
Gi0/2                  bpduguard          299
In this example, Gi0/2 is scheduled to recover in 299 seconds.
What Happens During Recovery
Once the timer expires, the port is automatically restored to the up/up state. The following logs illustrate the recovery process:
*Dec  8 15:30:45.261: %PM-4-ERR_RECOVER: Attempting to recover from bpduguard err-disable state on Gi0/2
*Dec  8 15:30:47.290: %LINK-3-UPDOWN: Interface GigabitEthernet0/2, changed state to up
*Dec  8 15:30:48.290: %LINEPROTO-5-UPDOWN: Line protocol on Interface GigabitEthernet0/2, changed state to up
Adjusting the Recovery Timer
We can adjust the default recovery timer of 300 seconds. You can modify it to any value between 30 and 86400 seconds.
If we check the available range:SW2(config)# errdisable recovery interval ? <30-86400> timer-interval(sec)For example, we set a custom interval of 30 seconds:
SW2(config)# errdisable recovery interval 30This timer applies to all active errdisable recovery causes.
Answer the question below
Which command enables automatic ErrDisable recovery for BPDU Guard?
BPDU Guard disables a port immediately if it receives a BPDU, as long as BPDU Guard is enabled on that port. This prevents unauthorized switches from interfering with the Spanning Tree topology.
Why it’s important – A single BPDU on an access port can disrupt STP. BPDU Guard stops it instantly.
How it behaves – When triggered, the port is placed into the err-disabled state (down/down).
How to configure it – Per port:
spanning-tree bpduguard enable| Globally:spanning-tree portfast bpduguard defaultHow to recover the port – Manually: using
shutdown/no shutdown| Automatically: witherrdisable recovery cause bpduguard
In the next lesson, we’ll explore BPDU Filter, a related feature that lets you control whether ports send or process BPDUs, giving you more flexibility in edge port behavior.
Answer the question below
Click 'Complete' to continue