In the previous lesson, you saw why GRE goes first and why IPsec runs in transport mode on top of it. Now you build both layers.
As the network engineer responsible for the New York (R1) and San Francisco (R2) sites, your task will be to configure the GRE over IPsec tunnel between them.
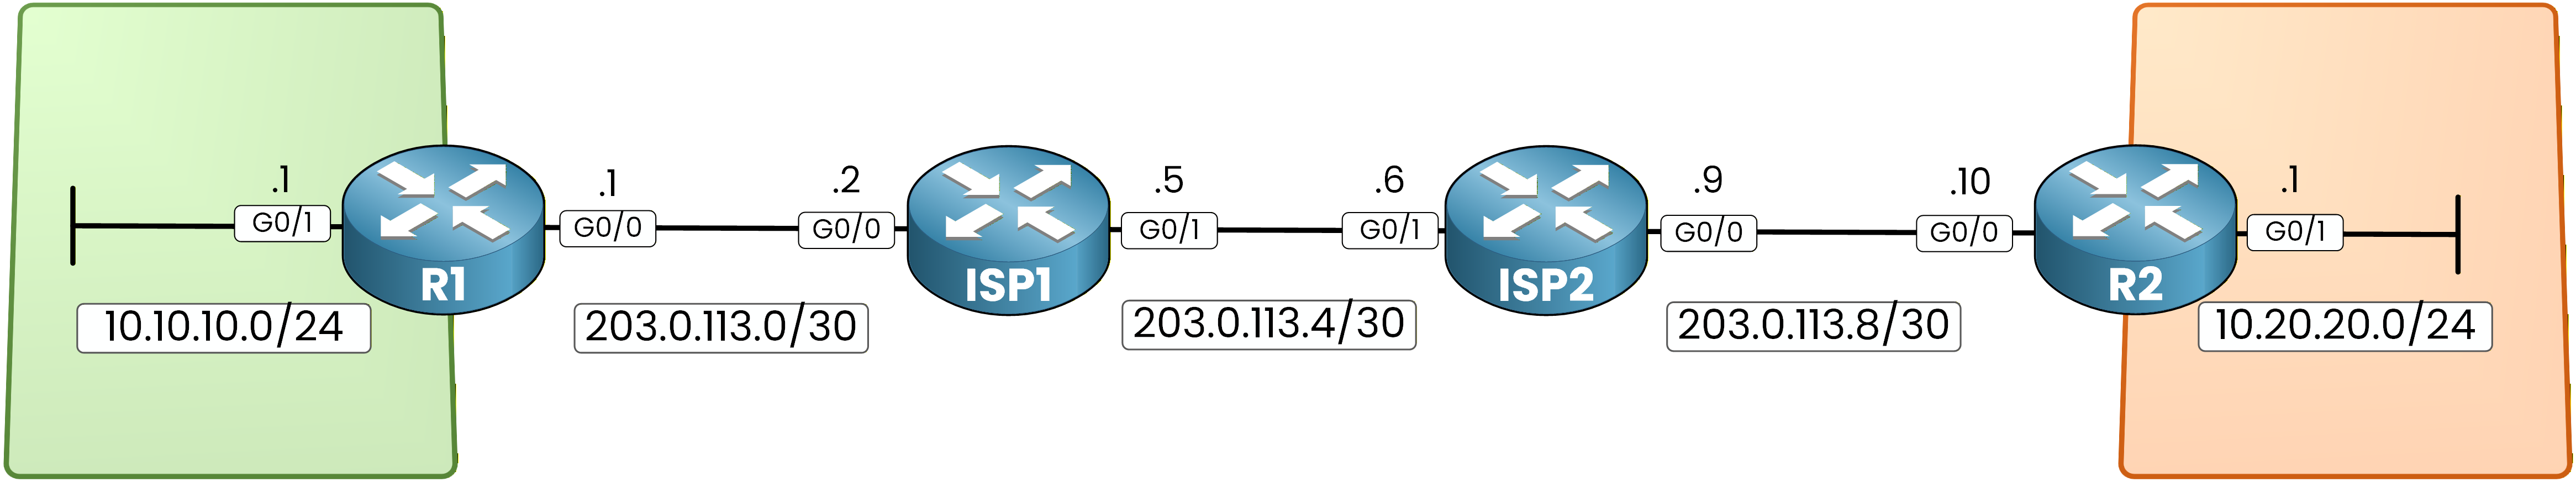
Figure 1 - GRE over IPsec lab topology
Underlay Routing
Before building the GRE tunnel, the underlay must be working.
Configure static routes on ISP1 and ISP2 so they can forward traffic between the two enterprise WAN interfaces.ISP1# conf t Enter configuration commands, one per line. End with CNTL/Z. ISP1(config)# ip route 10.10.10.0 255.255.255.0 203.0.113.1 ISP1(config)# ip route 10.20.20.0 255.255.255.0 203.0.113.6 ISP1(config)# ip route 203.0.113.8 255.255.255.252 203.0.113.6ISP2# conf t Enter configuration commands, one per line. End with CNTL/Z. ISP2(config)# ip route 10.10.10.0 255.255.255.0 203.0.113.5 ISP2(config)# ip route 10.20.20.0 255.255.255.0 203.0.113.10 ISP2(config)# ip route 203.0.113.0 255.255.255.252 203.0.113.5Each enterprise router also needs a default route toward its ISP.
R1(config)# ip route 0.0.0.0 0.0.0.0 203.0.113.2R2(config)# ip route 0.0.0.0 0.0.0.0 203.0.113.9GRE Tunnel
Your underlay is ready. Now build the GRE tunnel.
The tunnel endpoints are the WAN addresses and the tunnel uses the 192.168.100.0/30 subnet.On R1:
R1(config)# int tunnel0
%LINEPROTO-5-UPDOWN: Line protocol on Interface Tunnel0, changed state to down
R1(config-if)# ip address 192.168.100.1 255.255.255.252
R1(config-if)# tunnel source 203.0.113.1
R1(config-if)# tunnel destination 203.0.113.10
%LINEPROTO-5-UPDOWN: Line protocol on Interface Tunnel0, changed state to up
R1(config-if)# end
On R2:
R2(config)# int tunnel0
%LINEPROTO-5-UPDOWN: Line protocol on Interface Tunnel0, changed state to down
R2(config-if)# ip address 192.168.100.2 255.255.255.252
R2(config-if)# tunnel source 203.0.113.10
R2(config-if)# tunnel destination 203.0.113.1
%LINEPROTO-5-UPDOWN: Line protocol on Interface Tunnel0, changed state to up
%OSPF-5-ADJCHG: Process 1, Nbr 1.1.1.1 on Tunnel0 from LOADING to FULL, Loading Done
R2(config-if)# end
OSPF over GRE
The tunnel is up on both routers. The OSPF adjacency message on R2 confirms Hello packets are already flowing through GRE.
Now configure OSPF across the tunnel.R1(config)# router ospf 1 R1(config-router)# router-id 1.1.1.1 R1(config-router)# network 10.10.10.0 0.0.0.255 area 0 R1(config-router)# network 192.168.100.0 0.0.0.3 area 0 R1(config-router)# exitR2(config)# router ospf 1 R2(config-router)# router-id 2.2.2.2 R2(config-router)# network 10.20.20.0 0.0.0.255 area 0 R2(config-router)# network 192.168.100.0 0.0.0.3 area 0 R2(config-router)# exitYour GRE tunnel is up and OSPF is running through it.
But traffic is still in cleartext. Now add IPsec on top to encrypt it.Answer the question below
What subnet is used for the GRE tunnel addresses in this lab?
IPsec secures the GRE tunnel by encrypting GRE traffic as it crosses the Internet.
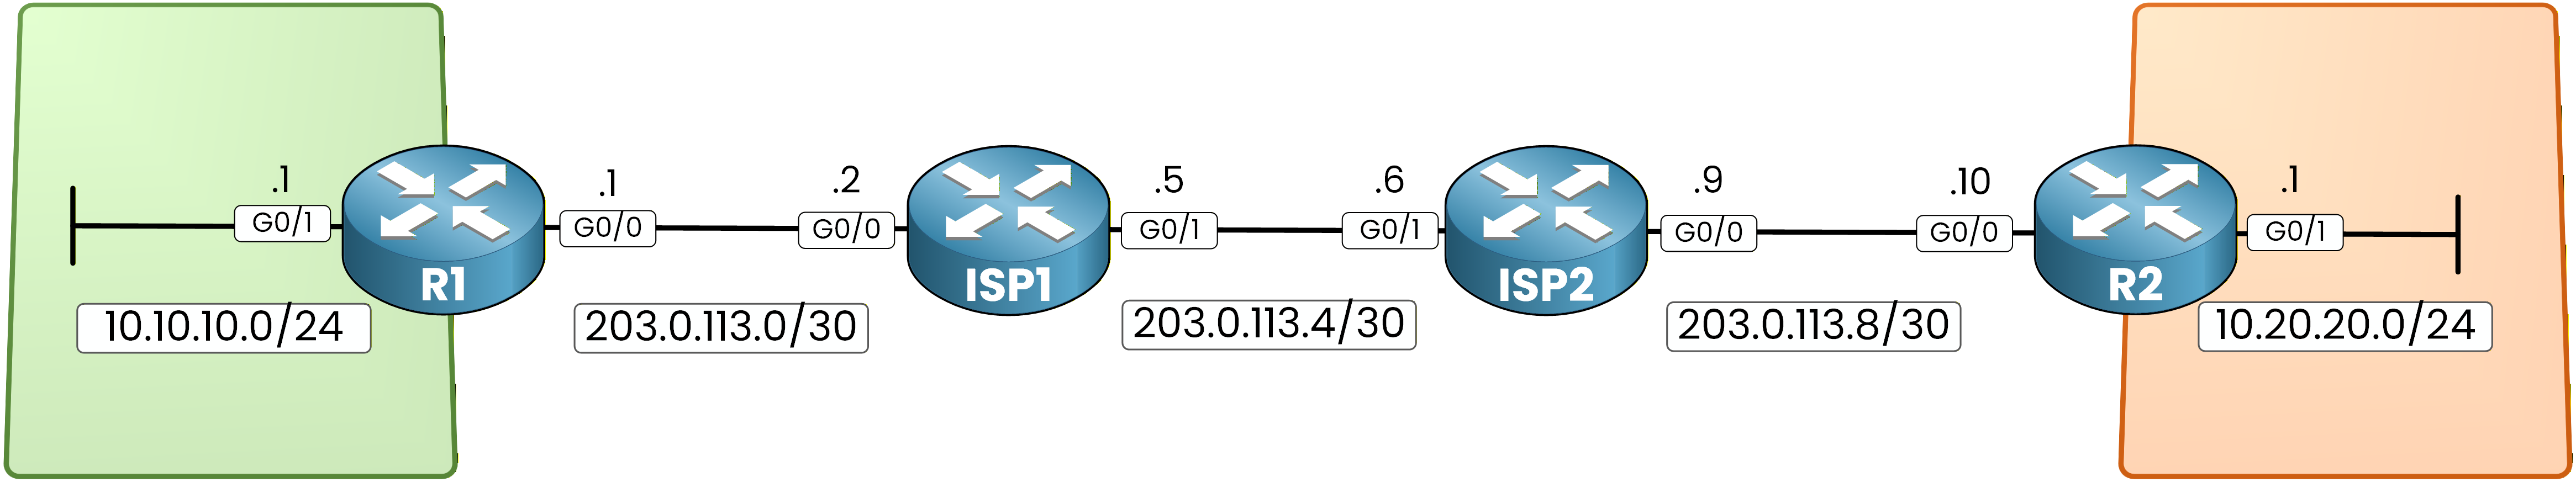
Figure 2 - GRE over IPsec lab topology
The workflow follows the same five steps as the IPsec Configuration lesson, with two key differences: the ACL matches GRE protocol 47 instead of LAN subnets, and the transform set uses transport mode instead of tunnel mode.
Step 1 - Interesting Traffic
Your ACL matches GRE protocol 47 between the two WAN addresses.
This tells IPsec to encrypt everything that belongs to the GRE tunnel.R1(config)# access-list 110 permit gre host 203.0.113.1 host 203.0.113.10R2(config)# access-list 110 permit gre host 203.0.113.10 host 203.0.113.1The ACLs are mirrored.
On R1 the source is its own WAN IP; on R2 it is the opposite.Step 2 - IKE Phase 1
R1(config)# crypto isakmp policy 1 R1(config-isakmp)# encryption aes R1(config-isakmp)# hash sha R1(config-isakmp)# authentication pre-share R1(config-isakmp)# group 14 R1(config-isakmp)# lifetime 86400 R1(config-isakmp)# exit R1(config)# crypto isakmp key cisco address 203.0.113.10R2(config)# crypto isakmp policy 1 R2(config-isakmp)# encryption aes R2(config-isakmp)# hash sha R2(config-isakmp)# authentication pre-share R2(config-isakmp)# group 14 R2(config-isakmp)# lifetime 86400 R2(config-isakmp)# exit R2(config)# crypto isakmp key cisco address 203.0.113.1Step 3 - Transform Set
For GRE over IPsec, transport mode is used.
The GRE header already provides the outer IP header so IPsec does not need to add another one.R1(config)# crypto ipsec transform-set GRE-IPSEC esp-aes esp-sha-hmac R1(cfg-crypto-trans)# mode transport R1(cfg-crypto-trans)# exitR2(config)# crypto ipsec transform-set GRE-IPSEC esp-aes esp-sha-hmac R2(cfg-crypto-trans)# mode transport R2(cfg-crypto-trans)# exitStep 4 - Crypto Map
R1(config)# crypto map VPN-IPSEC 10 ipsec-isakmp R1(config-crypto-map)# set peer 203.0.113.10 R1(config-crypto-map)# set transform-set GRE-IPSEC R1(config-crypto-map)# match address 110 R1(config-crypto-map)# exitR2(config)# crypto map VPN-IPSEC 10 ipsec-isakmp R2(config-crypto-map)# set peer 203.0.113.1 R2(config-crypto-map)# set transform-set GRE-IPSEC R2(config-crypto-map)# match address 110 R2(config-crypto-map)# exitStep 5 - Apply to Interface
R1(config)# interface g0/0 R1(config-if)# crypto map VPN-IPSEC %CRYPTO-6-ISAKMP_ON_OFF: ISAKMP is ON %LINEPROTO-5-UPDOWN: Line protocol on Interface NVI0, changed state to upR2(config)# interface g0/0 R2(config-if)# crypto map VPN-IPSEC %CRYPTO-6-ISAKMP_ON_OFF: ISAKMP is ON %LINEPROTO-5-UPDOWN: Line protocol on Interface NVI0, changed state to upThe ISAKMP is ON message confirms IKE is active on the WAN interface.
Your GRE tunnel is running and IPsec is encrypting every GRE packet crossing the Internet.Answer the question below
In the transform set, what mode keyword replaces tunnel for GRE over IPsec?
Answer the question below
With HQ at WAN 198.51.100.1 and LAN 172.16.1.0/24, which destination must Branch's crypto ACL match?
Your configuration is complete.
Now verify the GRE tunnel is up, OSPF is running through it, and IPsec is encrypting your GRE traffic. You will run all checks on R1 first, then on R2.Verification on R1
R1# show ip int brief
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         203.0.113.1     YES NVRAM  up                    up
GigabitEthernet0/1         10.10.10.1      YES NVRAM  up                    up
GigabitEthernet0/2         unassigned      YES NVRAM  administratively down down
GigabitEthernet0/3         unassigned      YES NVRAM  administratively down down
NVI0                       203.0.113.1     YES unset  up                    up
Tunnel0                    192.168.100.1   YES manual up                    up
Tunnel0 is up at 192.168.100.1.
The NVI0 interface appears when you apply a crypto map: it confirms IPsec is active.R1# show ip ospf neighbor Neighbor ID Pri State Dead Time Address Interface 2.2.2.2 0 FULL/ - 00:00:34 192.168.100.2 Tunnel0OSPF neighbor 2.2.2.2 is in FULL state through Tunnel0.
Routing protocol traffic is flowing inside your encrypted GRE tunnel.R1# show ip route Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area Gateway of last resort is 203.0.113.2 to network 0.0.0.0 S* 0.0.0.0/0 [1/0] via 203.0.113.2 10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks C 10.10.10.0/24 is directly connected, GigabitEthernet0/1 L 10.10.10.1/32 is directly connected, GigabitEthernet0/1 O 10.20.20.0/24 [110/1001] via 192.168.100.2, 00:03:52, Tunnel0 192.168.100.0/24 is variably subnetted, 2 subnets, 2 masks C 192.168.100.0/30 is directly connected, Tunnel0 L 192.168.100.1/32 is directly connected, Tunnel0 203.0.113.0/24 is variably subnetted, 2 subnets, 2 masks C 203.0.113.0/30 is directly connected, GigabitEthernet0/0 L 203.0.113.1/32 is directly connected, GigabitEthernet0/0R1# ping 10.20.20.1 source 10.10.10.1 Type escape sequence to abort. Sending 5, 100-byte ICMP Echos to 10.20.20.1, timeout is 2 seconds: Packet sent with a source address of 10.10.10.1 !!!!! Success rate is 100 percent (5/5), round-trip min/avg/max = 6/9/15 msR1# show crypto ipsec sa interface: GigabitEthernet0/0 Crypto map tag: VPN-IPSEC, local addr 203.0.113.1 local ident (addr/mask/prot/port): (203.0.113.1/255.255.255.255/47/0) remote ident (addr/mask/prot/port): (203.0.113.10/255.255.255.255/47/0) #pkts encaps: 54, #pkts encrypt: 54, #pkts digest: 54 #pkts decaps: 53, #pkts decrypt: 53, #pkts verify: 53 #send errors 0, #recv errors 0 inbound esp sas: in use settings ={Transport, } Status: ACTIVE(ACTIVE) outbound esp sas: in use settings ={Transport, } Status: ACTIVE(ACTIVE)local/remote ident prot: 47 — IPsec is protecting GRE protocol 47, not raw IP subnets
in use settings ={Transport, } — transport mode is active, not tunnel mode
#pkts encaps: 54, #pkts encrypt: 54 — GRE packets are being encrypted and sent
R1# show crypto session
Crypto session current status

Interface: GigabitEthernet0/0
Session status: UP-ACTIVE
Peer: 203.0.113.10 port 500
  IPSEC FLOW: permit 47 host 203.0.113.1 host 203.0.113.10
        Active SAs: 4, origin: crypto map
Session status is UP-ACTIVE. The IPSEC FLOW confirms permit 47 is protected.
Active SAs: 4 shows Phase 1 and Phase 2 are fully established.Verification on R2
R2# show ip int brief Interface IP-Address OK? Method Status Protocol GigabitEthernet0/0 203.0.113.10 YES NVRAM up up GigabitEthernet0/1 10.20.20.1 YES NVRAM up up NVI0 203.0.113.10 YES unset up up Tunnel0 192.168.100.2 YES NVRAM up upR2# show interfaces tunnel0 Tunnel0 is up, line protocol is up Hardware is Tunnel Internet address is 192.168.100.2/30 Tunnel source 203.0.113.10, destination 203.0.113.1 Tunnel protocol/transport GRE/IP Tunnel transport MTU 1476 bytes 160 packets input, 16740 bytes, 0 no buffer 0 input errors 199 packets output, 20756 bytes, 0 underruns 0 output errorsR2# show ip ospf neighbor Neighbor ID Pri State Dead Time Address Interface 1.1.1.1 0 FULL/ - 00:00:33 192.168.100.1 Tunnel0R2# show crypto session Crypto session current status Interface: GigabitEthernet0/0 Session status: UP-ACTIVE Peer: 203.0.113.1 port 500 IPSEC FLOW: permit 47 host 203.0.113.10 host 203.0.113.1 Active SAs: 4, origin: crypto mapR2# show crypto ipsec sa interface: GigabitEthernet0/0 Crypto map tag: VPN-IPSEC, local addr 203.0.113.10 local ident (addr/mask/prot/port): (203.0.113.10/255.255.255.255/47/0) remote ident (addr/mask/prot/port): (203.0.113.1/255.255.255.255/47/0) #pkts encaps: 81, #pkts encrypt: 81, #pkts digest: 81 #pkts decaps: 82, #pkts decrypt: 82, #pkts verify: 82 #send errors 0, #recv errors 0 inbound esp sas: in use settings ={Transport, } Status: ACTIVE(ACTIVE) outbound esp sas: in use settings ={Transport, } Status: ACTIVE(ACTIVE)R2# show crypto isakmp sa IPv4 Crypto ISAKMP SA dst src state conn-id status 203.0.113.1 203.0.113.10 QM_IDLE 1001 ACTIVE 203.0.113.10 203.0.113.1 QM_IDLE 1002 ACTIVE IPv6 Crypto ISAKMP SABoth ISAKMP SAs show QM_IDLE / ACTIVE.
Two entries appear because both routers initiated a session.
Both sides confirm the same result: GRE tunnel up, IPsec encrypting protocol 47 in transport mode, OSPF in FULL state.
Your GRE over IPsec tunnel is fully operational.Answer the question below
In show crypto ipsec sa, what value appears in "in use settings" when transport mode is active?