Dynamic NAT (Network Address Translation) allows internal devices using private IP addresses to access external networks using a shared pool of public IP addresses.
Instead of assigning a fixed public IP to each device (like Static NAT), Dynamic NAT uses a temporary 1-to-1 mapping between private and public IPs.
As you can see below, our NAT router has a public IP pool of three addresses:

Figure 1 – Dynamic NAT assigns a temporary public IP from a shared pool when a device sends traffic
37.5.55.103
37.5.55.104
37.5.55.105
When a device from the internal network sends traffic to the internet, the router checks if a public IP is available in the pool. If one is free, it is assigned for the duration of the session. When the device stops sending traffic, the public IP is released back into the pool.
You can think of it as a temporary borrowing system: if a public IP is available, the device gets one just for the time it needs.
Answer the question below
How many public IPs are in the pool?
Let's walk through a concrete example.
Suppose host 192.168.1.6 wants to reach the server 8.8.8.8 on the internet.
The NAT router checks the pool of public IP addresses.If one is available, it temporarily assigns it to 192.168.1.6 and forwards the traffic.

Figure 2 – Outgoing packet from internal host
The router maps 192.168.1.6 to 37.5.55.103, showing the traffic going out.

Figure 3 – NAT translation applied
When the session ends or becomes inactive, the router removes the mapping and returns the public IP to the pool.

Figure 4 – Public IP released
The public IP 37.5.55.103 is now free again for use by another device.
This process follows first-come, first-served logic:
only one internal host can use a specific public IP at a time.
If all public IPs are in use, new connections are denied.Answer the question below
Which public IP does the router assign to 192.168.1.6?
Let's now configure Dynamic NAT on a Cisco router. This setup enables multiple internal devices to access the internet using a limited set of public IPs.

Figure 5 – Configuring Dynamic NAT on a Cisco Router
Step 1 – Define the internal and external interfaces
We need to indicate which interface connects to the internal (private) network, and which one connects to the external (public) side:
NAT# conf t
Enter configuration commands, one per line.  End with CNTL/Z.
NAT(config)# int g0/0
NAT(config-if)# ip address 192.168.1.254 255.255.255.0
NAT(config-if)# ip nat inside
NAT(config-if)# exit

NAT(config)# int g0/1
NAT(config-if)# ip address 37.5.55.1 255.255.255.0
NAT(config-if)# ip nat outside
NAT(config-if)# exit
Step 2 – Create an access list for devices allowed to use NAT
This access list targets internal IPs that will be translated (an access list, or ACL, is a filter that matches addresses; ACLs get their own module later in this path):
NAT(config)# ip access-list standard LOCAL_HOSTS
NAT(config-std-nacl)# permit 192.168.1.0 0.0.0.255
NAT(config-std-nacl)# exit
Step 3 – Define the NAT Address Pool
Here, we define the range of external IPs that the router can assign temporarily:
NAT(config)# ip nat pool PUBLIC_POOL 37.5.55.103 37.5.55.105 netmask 255.255.255.0Step 4 – Bind the NAT rule to the access list and pool
Now we tell the router: “Translate the internal IPs defined in the access list using the public pool.”
NAT(config)# ip nat inside source list LOCAL_HOSTS pool PUBLIC_POOLAnswer the question below
Which command creates a pool of public IP addresses for NAT?
Let's test the NAT behavior in action.
Step 1 – Simulate real traffic from inside
We send a ping from PC2 (192.168.1.6) to a public server (8.8.8.8):
PC2> ping 8.8.8.8
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 8.8.8.8, timeout is 2 seconds:
.!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/2/6 ms
This triggers the NAT router to temporarily assign a public IP to PC2.
Step 2 – Display the current translations
On the router, run:
NAT# show ip nat translations

Pro  Inside global     Inside local       Outside local     Outside global
icmp 37.5.55.103:3     192.168.1.6:3      8.8.8.8:3         8.8.8.8:3
--- 37.5.55.103        192.168.1.6        ---               ---
This confirms that:
192.168.1.6 was mapped to 37.5.55.103
The router handles the NAT translation during the session
When the session ends, the mapping disappears automatically
Step 3 – Check global NAT usage and statistics
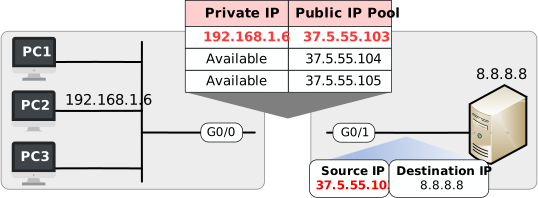
Figure 6 – NAT translation in action and statistics
To see overall activity and NAT pool usage:
NAT# show ip nat statistics
Total active translations: 1 (0 static, 1 dynamic; 1 extended)
Outside interfaces:
  GigabitEthernet0/1
Inside interfaces:
  GigabitEthernet0/0
Hits: 1  Misses: 0
CEF Translated packets: 1, CEF Punted packets: 0
Reserved port setting disabled provisioned no
Expired translations: 0
Dynamic mappings:
-- Inside Source
[Id: 1] access-list LOCAL_HOSTS pool PUBLIC_POOL refcount 1
 pool PUBLIC_POOL: netmask 255.255.255.0
     start 37.5.55.103 end 37.5.55.105
     type generic, total addresses 3, allocated 1 (33%), misses 0
nat-limit statistics:
 max entry: max allowed 0, used 0, missed 0
We now know:
1 IP is dynamically used from the public pool
NAT is functioning properly
No dropped connections occurred
Answer the question below
Which command shows the current NAT translations on a Cisco router?
Answer the question below
If PUBLIC_POOL were recreated to run from 37.5.55.103 to 37.5.55.110, what total addresses value would show ip nat statistics print?
Answer the question below
A fourth inside host tries to go out while all three pool addresses are allocated: which counter on the pool PUBLIC_POOL line increases from 0?
Dynamic NAT is a step forward compared to Static NAT, but it still has major limitations.
Let's say you have only three public IP addresses in your NAT pool. That means only three internal devices can access the internet at the same time. Once those IPs are used, any new connection attempt will be dropped.
This creates a serious scalability problem:
You need to own a large block of public IPs to support many users.
Each session consumes one public IP address.
This makes Dynamic NAT unsuitable for large networks, such as schools, businesses, or service providers.
Dynamic NAT helps temporarily, but it still depends heavily on how many public IPs you have available.
What's the solution?
To solve this issue, networks use PAT (Port Address Translation), also called NAT Overload.
Instead of requiring one public IP per device, PAT allows hundreds of internal hosts to share a single public IP, by mapping different port numbers.
We'll explore how PAT works and how it solves Dynamic NAT's limitations, right after the Dynamic NAT lab.
Answer the question below
Click 'Complete' to continue